Sign up free, get an access key
Create a splitforms account with email + password. Your access key appears in the dashboard immediately. No credit card required.
Spam-free contact form
Block 95–99% of bot and junk submissions with a no-CAPTCHA honeypot, a time-trap, and server-side filters — your visitors never see a puzzle, and nothing third-party loads in their browser.
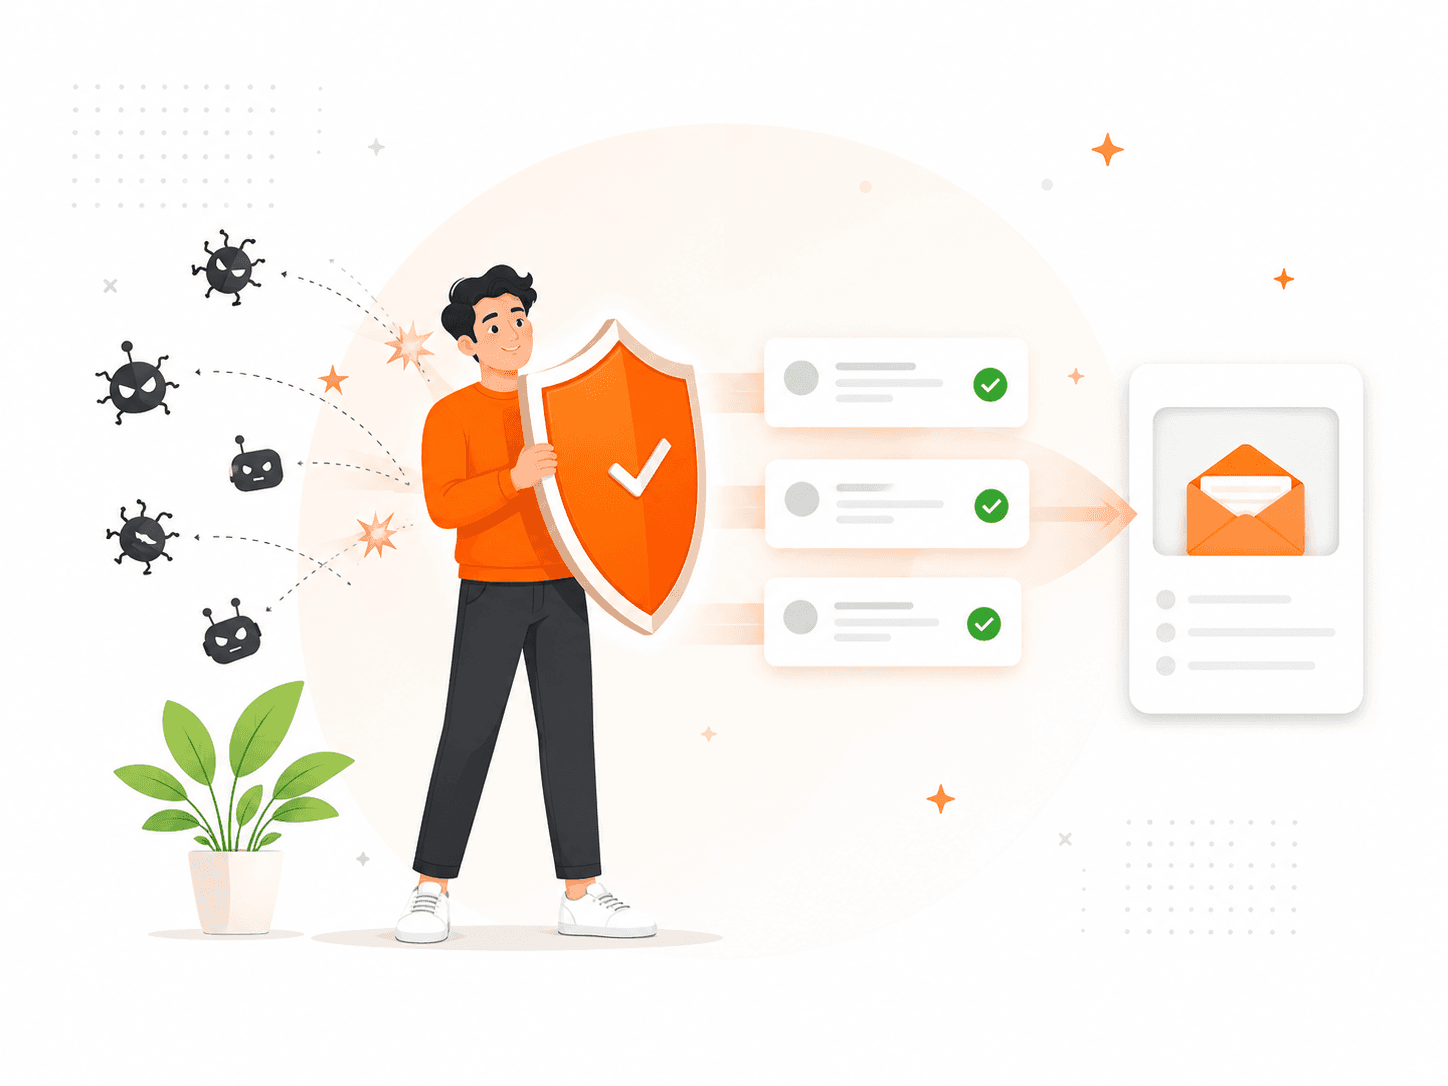
A hidden botcheck field bots fill and real visitors never see — dropped before it reaches your inbox.
A bot fills a form in ~50ms, so submissions completed in under two seconds are auto-rejected.
Filtering is 100% server-side — visitors are never challenged, and nothing third-party loads.
Copy-paste ready
This is the whole form — the two hidden fields do the work. The botcheck honeypot catches bots that fill every input, and the form_loaded_at time-trap rejects anything submitted in under two seconds. Replace YOUR_ACCESS_KEY with your key and paste it into any HTML page, React component, or Webflow embed. Submitting via fetch()? See the React & Next.js spam guide.
<form action="https://splitforms.com/api/submit" method="POST">
  <input type="hidden" name="access_key" value="YOUR_ACCESS_KEY" />

  <input type="text"  name="name"    placeholder="Name"    required />
  <input type="email" name="email"   placeholder="Email"   required />
  <textarea           name="message" placeholder="Message" required></textarea>

  <!-- 1. Honeypot — hidden from real users, bots fill it in -->
  <input type="checkbox" name="botcheck" style="display:none" tabindex="-1" autocomplete="off" />

  <!-- 2. Time-trap — submissions faster than 2s are auto-rejected -->
  <input type="hidden" name="form_loaded_at" value="" />
  <script>
    document.currentScript.previousElementSibling.value = Date.now();
  </script>

  <button type="submit">Send message</button>
</form>
Setup
Sixty seconds, no plugin, no CAPTCHA — the same three steps whether you paste the form into raw HTML, a React component, a Webflow embed, or a WordPress Custom HTML block.
Create a splitforms account with email + password. Your access key appears in the dashboard immediately. No credit card required.
Copy the snippet and drop it into any HTML page, React component, Webflow embed, or WordPress Custom HTML block. The hidden botcheck and form_loaded_at fields arm two of the spam filters automatically.
Every submission runs through the honeypot, time-trap, IP rate limit, content heuristics, and your domain allow-list in under 50ms. Clean messages hit your dashboard; Free includes inbox delivery. Spam is dropped or quarantined to the Spam folder.
The defense
No single trick stops every bot, so splitforms runs five server-side filters together on every submission — in under 50 milliseconds, with nothing loading in your visitor's browser. Read the complete spam-protection guide or the full spam-protection feature.
No CAPTCHA
The reflex fix is to bolt on reCAPTCHA — but it taxes every legitimate visitor with friction, blocks screen-reader and low-vision users, and sets Google cookies that become a GDPR headache. A spam-free form lets the bot convict itself instead: a honeypot it fills, a timer it beats, an IP it floods, a message that scores like spam — removing 95–99% of spam invisibly and keeping the page GDPR-clean. Read contact form without CAPTCHA and honeypot vs reCAPTCHA.
How SplitForms works
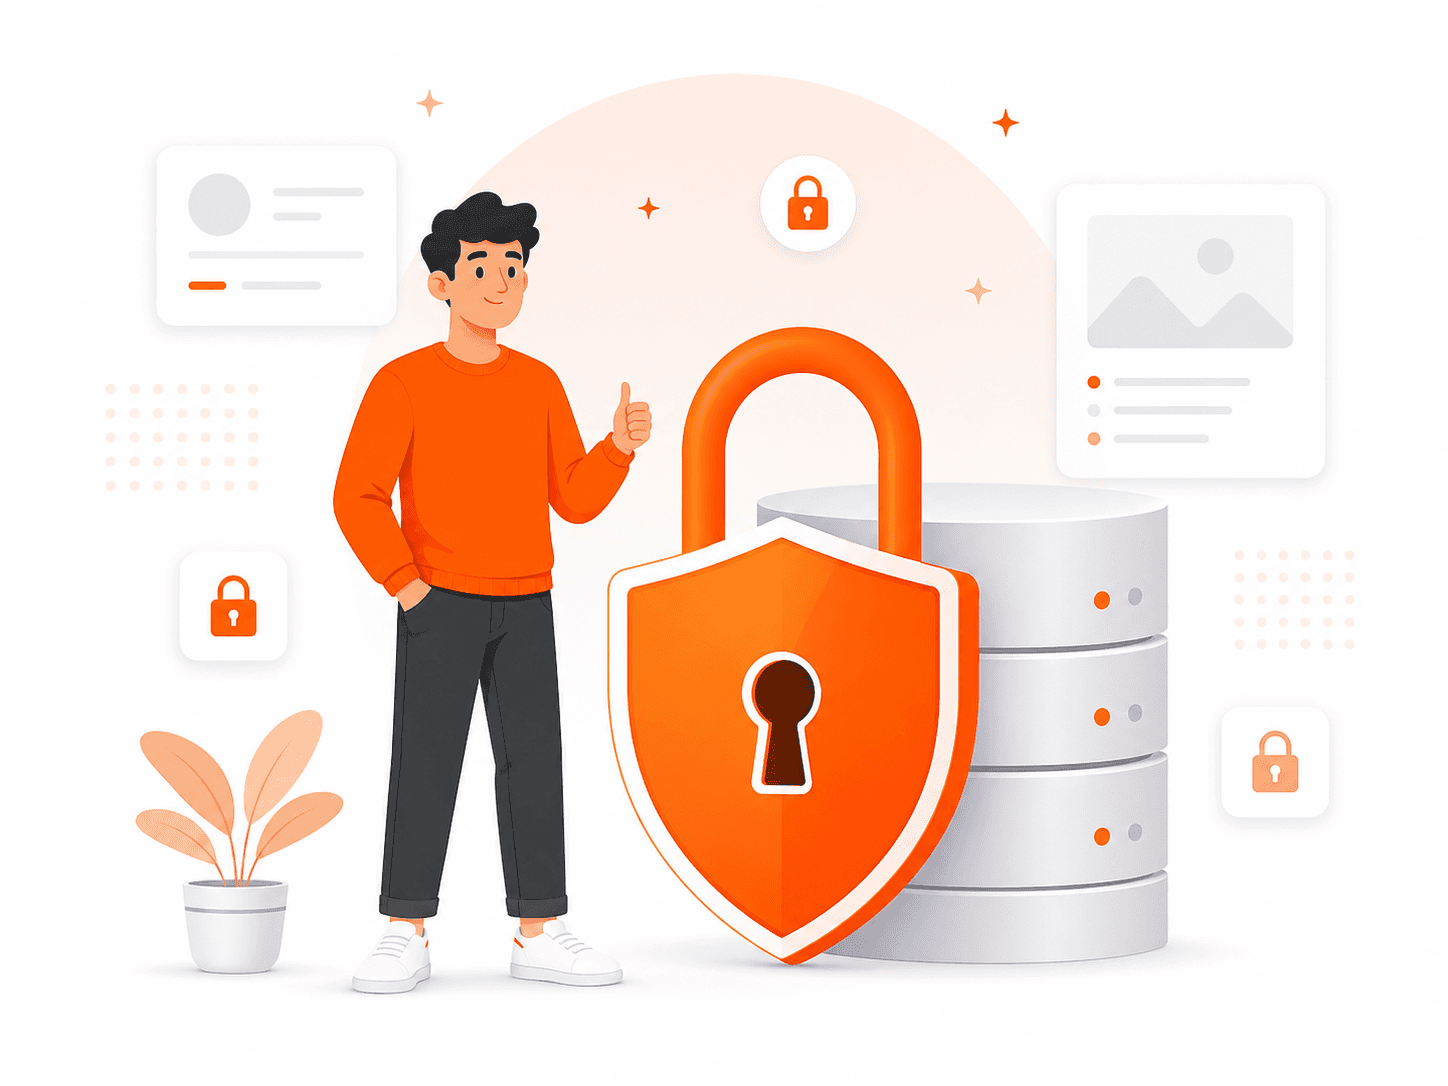
Connect your form, collect every submission, and send data where it needs to go — without building backend infrastructure.
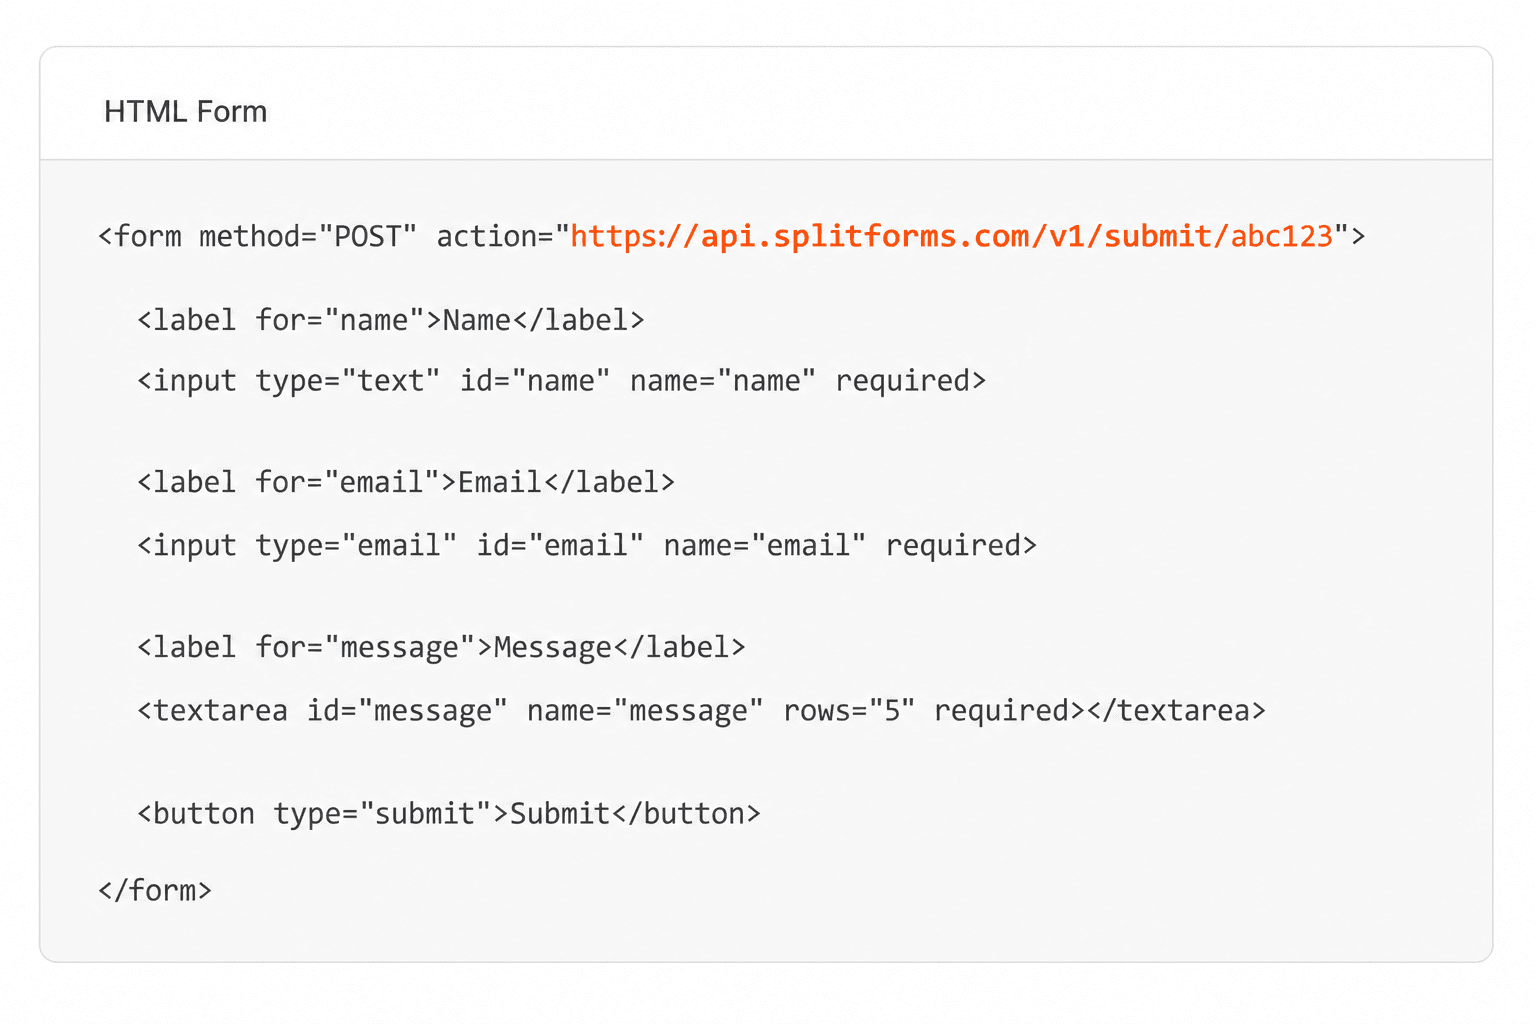
Point your form to your unique SplitForms endpoint. That's it.
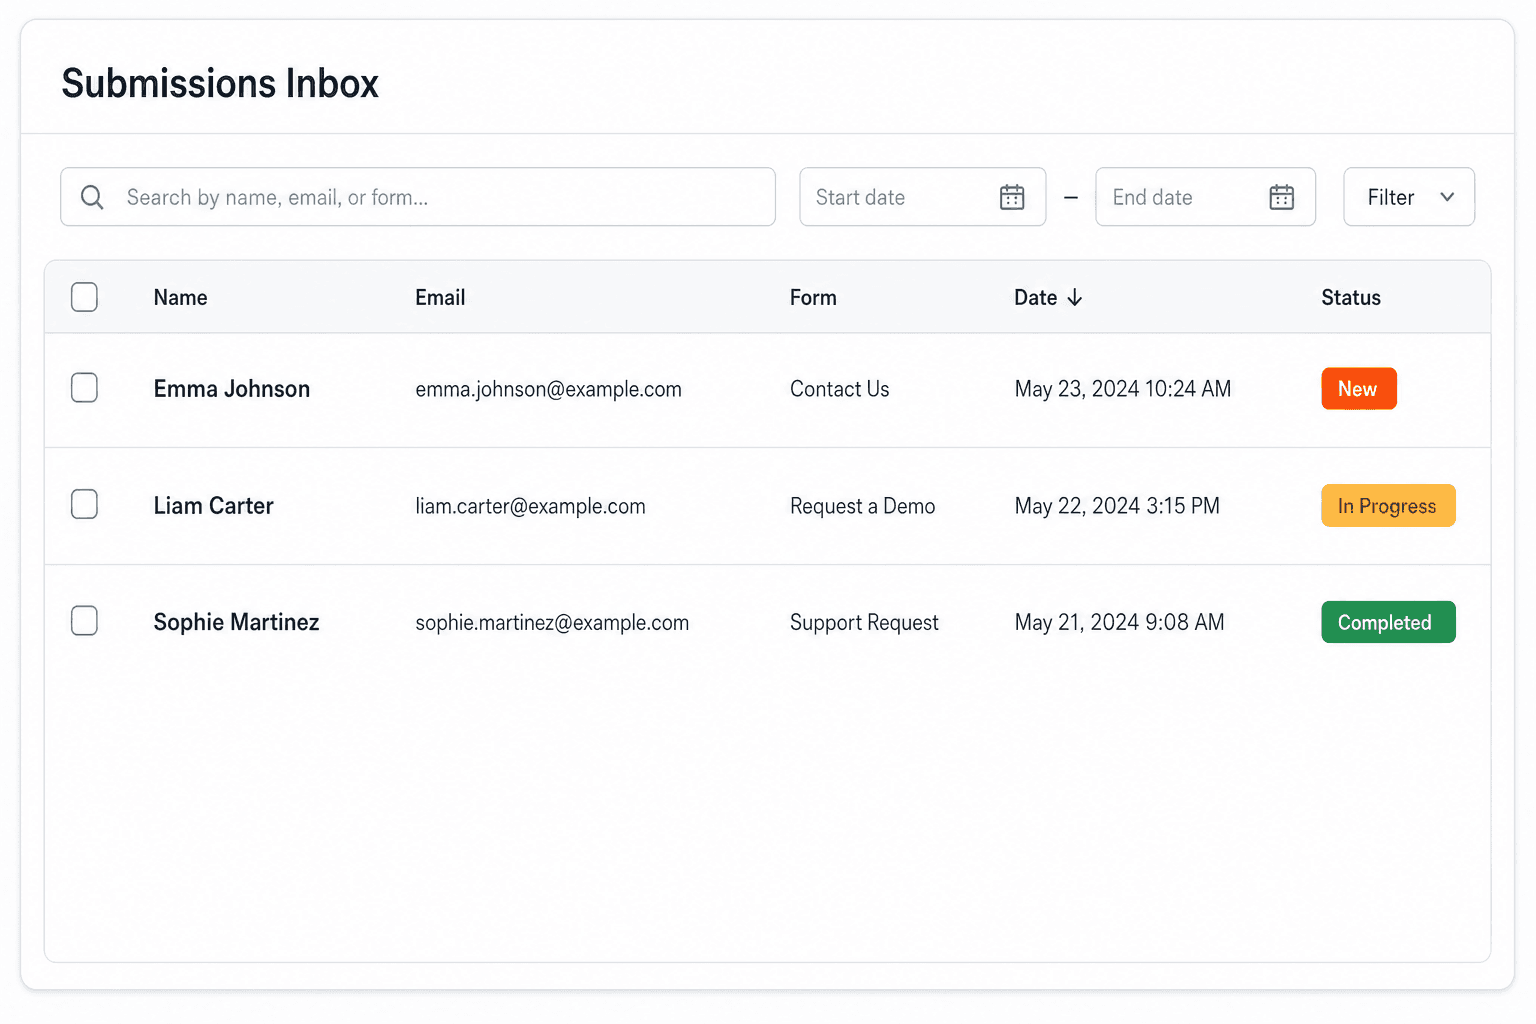
We instantly capture and organize every submission in your inbox.
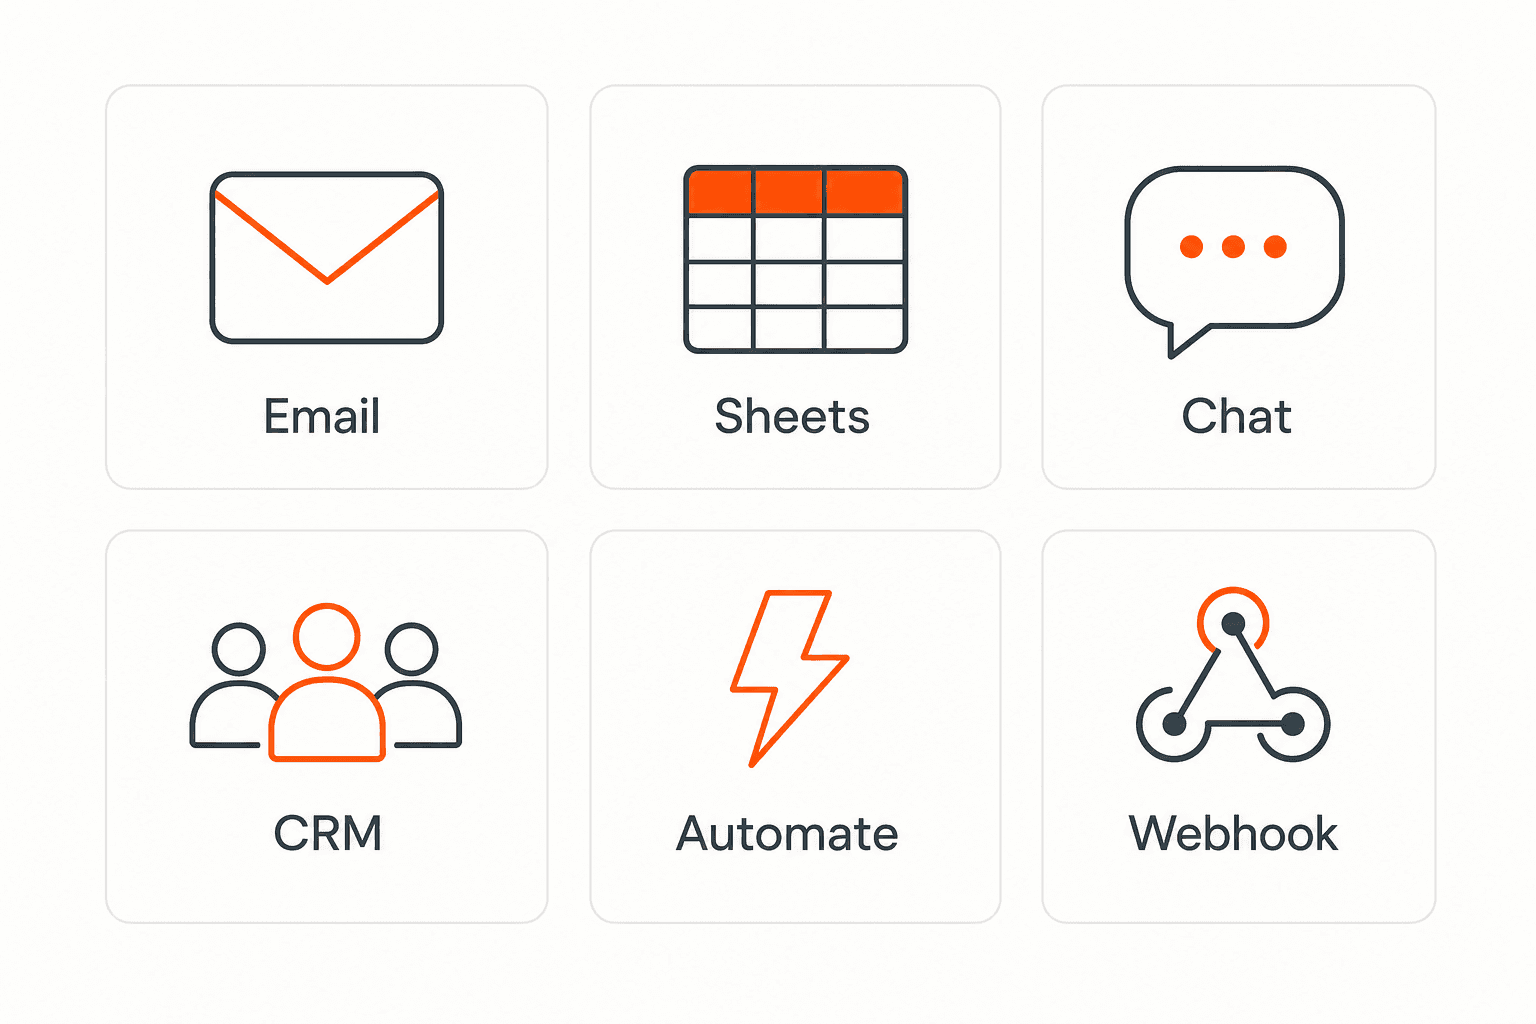
Send data to email, spreadsheets, CRMs, webhooks, and 7,000+ apps.
No credit card required. Set up in under 60 seconds.
Connect & automate
SplitForms works with the destinations you route to and the platforms you build on — from Slack and Sheets to WordPress, Shopify, and Next.js. And with Stripe connected, your forms can take payments too.
 NewTake payments on your formsDeposits, bookings, order forms — submitters check out through Stripe and the money goes straight to your Stripe account. Included on every paid plan.See plans →
Trusted by indie teams and agencies shipping forms worldwide
Testimonials
40 quotes on record — from indie hacks to agency migrations.
“I replaced a Lambda + DynamoDB + SES contact form with six lines of HTML. It took eleven minutes, and the dashboard is better than what I was going to build.”
“We migrated 14 client sites off Formspree in a single weekend. The price is a third of what we paid, the API is more honest, and the spam filter actually works.”
“The webhook payload is signed, idempotent, and well-shaped. It reads like code from a competent team, not a CRUD app held together with duct tape.”
“I stopped reaching for Typeform on small marketing sites. splitforms covers 90% of the use case at none of the bloat.”
“I onboarded our whole agency in an afternoon. The MCP integration meant Cursor literally dropped the form straight into our client repos for us.”
“The free plan gave me 200 submissions before I paid a cent, and Pro is five dollars a month. I've spent more on coffee deciding which backend to use.”
“Spam went from forty junk entries a day to zero, with no reCAPTCHA puzzle ruining the form. The honeypot and time-trap just quietly do their job.”
“Point the form action at one endpoint and you're done. No SDK, no client library, no build step. This is how a form backend should feel.”
“Leads land in Slack the second someone submits, and a copy goes to Google Sheets for the sales team. I wired both up in under ten minutes.”
“I run a static Hugo site on a five-dollar VPS. splitforms gave it a real contact form without me standing up a single server.”
Questions
A spam-free contact form filters out automated and low-quality submissions before they reach you, so your inbox only shows real messages. splitforms does this with a layered server-side defense — honeypot, time-trap, IP rate limiting, and content heuristics — that runs on every POST to splitforms.com/api/submit in under 50ms. Typical sites stop 95–99% of spam at the edge. No form is 100% spam-proof forever, but layered filtering removes the overwhelming majority with no work on your side.
No. There is no CAPTCHA, no reCAPTCHA checkbox, and no "select all the traffic lights" puzzle. The defense is entirely server-side, so your visitors never get challenged and your conversion rate doesn't take the hit that CAPTCHAs cause. If you specifically want a CAPTCHA you can still add reCAPTCHA, hCaptcha, or Turnstile on top, but it isn't required to stop spam.
Typical sites block 95–99% of spam before it ever reaches an inbox or webhook. The honeypot alone catches roughly 85% of the cheap, high-volume bots; adding the time-trap and the content-heuristics layer lifts that to the 95–99% range. It works on the very first submission — there is no training period and no script to load.
Yes — every layer (honeypot, time-trap, IP rate limit, content heuristics, domain allow-list, and the Spam queue) is included on the Free 200-submissions plan, and email notifications to you are free on every plan too. There is no upsell for spam filtering. Paid plans add exports, webhooks/integrations, and an auto-responder, but the filtering itself is identical at every tier.
It's tuned to avoid that, and the edge cases are handled: the honeypot is aria-hidden and tabindex=-1 so screen readers and keyboard users skip it; back-button re-submits and password-manager autofill are accounted for; and slow legitimate forms (job applications, long surveys) can raise the time-trap threshold per form. On the rare occasion something real is filtered, it lands in the dashboard's Spam folder and you recover it — and its notification email — in one click from the Spam queue.
Yes. The filtering is server-side, so it doesn't care what rendered the form. Anywhere you can paste HTML — a WordPress Custom HTML block, a Webflow embed, a Carrd element, a Squarespace code block — the spam-free form works without a plugin. For React, Next.js, Vue, or any SPA that submits via fetch(), send an empty botcheck field and a form_loaded_at timestamp and the same protection applies.
Yes. Because there's no Google reCAPTCHA, there are no reCAPTCHA cookies, no device fingerprinting, and no third-party JavaScript executing in your visitors' browsers — three of the most common GDPR headaches with CAPTCHA-based spam protection. Notification emails are sent from a warmed, SPF/DKIM/DMARC-aligned sender so they land in the inbox rather than a spam folder.
That's exactly why the defense is layered rather than a single trick. A honeypot is blind to headless-browser bots and human-looking, AI-generated messages submitted through the real form — so the content-heuristics layer scores the message text itself (link spam, repeated phrases, banned TLDs, gibberish), and strict-origin mode stops a leaked access key from being replayed on someone else's site. No system stops a determined attacker writing a bot for your specific form, but layered, server-side filtering keeps even that under control — and anything that slips through still lands in the Spam queue for one-click recovery.
Simple pricing
Choose a plan that fits your workflow — from a free form endpoint to full automations, exports, Stripe payments, and higher submission limits.
For side projects and indie devs.
For agencies and growing products.
Pay $59. 3 years sorted.
No credit card required on Free • Cancel anytime


